
 Multi-Vendor & Complex SaaS Marketplaces
 Modern Headless & Jamstack Web Development
 High-End Corporate & Specialized Business Websites
 Advanced API, Checkout & Database Troubleshooting
Stripping Sneaky Root Cloud Access: IAM Privilege Audit
Over-privileged IAM roles turn a minor automation app into a full-environment risk. This guide shows Australian teams how to audit sneaky root-level rights, enforce least privilege, and know when to book Fixwebnode for a remote hardening pass.
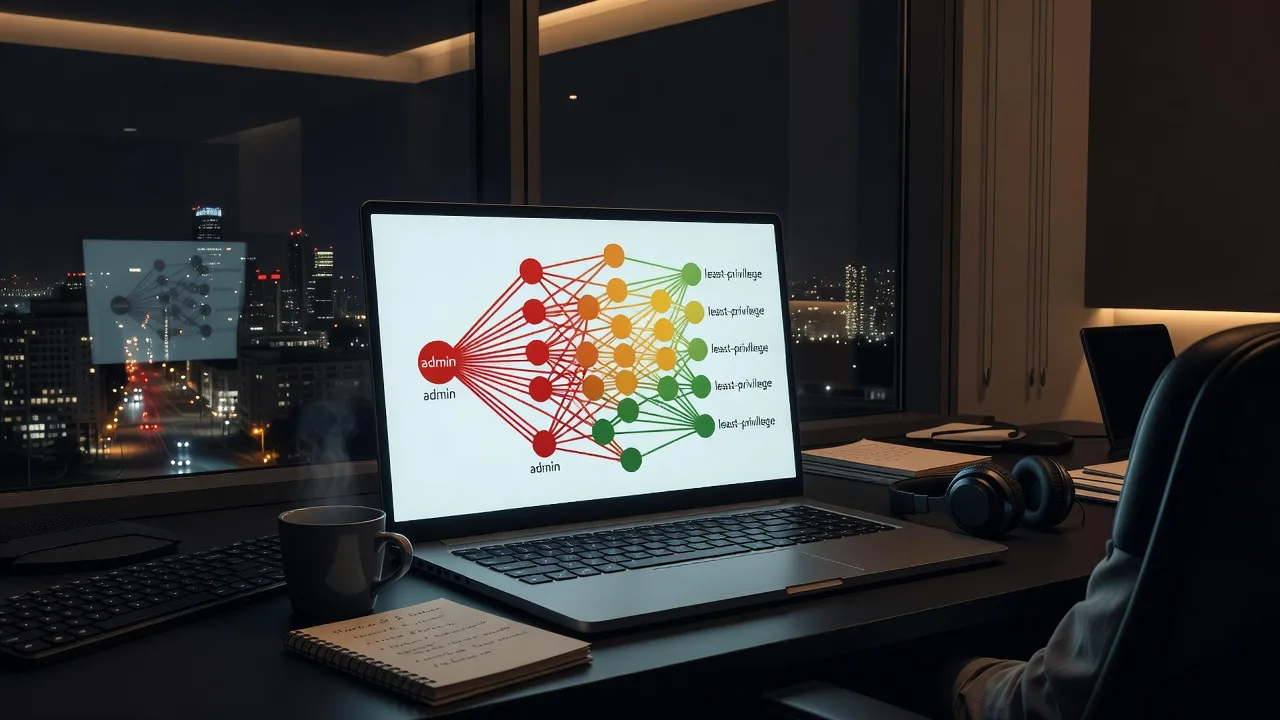
A minor backend automation app does not need full administrative permissions to your entire cloud environment. Let’s audit this access before it gets compromised. If you run workloads in AWS, Azure, or GCP from Australia—whether you are a sole trader, small business, or ops lead—over-privileged IAM roles are one of the fastest paths from a single key leak to a full account takeover. This practical guide walks you through The Over-Privileged IAM Role Audit: finding sneaky root-equivalent rights, stripping them safely, and enforcing least privilege across your corporate infrastructure. Fixwebnode delivers this work remotely for Australian operators; start at Fixwebnode website repair Australia when you want a specialist pass rather than a DIY-only cleanup.
Why does my automation role still have AdministratorAccess in Australia?
Most teams grant broad admin policies “just for now” during a rush deploy, then never revisit them. In Australia that often shows up as long-lived access keys on EC2/Lambda roles, wildcard Resource: "*" statements, and unused services still attached to production principals. Fix the role scope first; rotating secrets alone will not stop lateral movement if the role can still create users or disable logging.
| Symptom | Quick fix | When to call Fixwebnode |
|---|---|---|
| Role has AdministratorAccess or *:* | Detach managed admin; attach scoped inline/managed policy | Unclear blast radius or production lockout risk |
| Access keys unused for 90+ days | Deactivate, then delete after verification | Keys embedded in unknown apps or CI |
| CloudTrail shows iam:PassRole / CreateUser from automation | Remove identity-admin actions; add explicit Deny | Active suspicious API calls or missing logs |
Why over-privileged IAM roles matter more than you think
Principle of least privilege is not a checkbox—it is the difference between a compromised job token deleting one queue and that same token disabling CloudTrail, creating a backdoor user, and exfiltrating S3. Australian organisations also face practical pressure: shared “devops” roles across staging and prod, contractors who left with keys still active, and SaaS integrations that requested admin “to simplify setup.” The Over-Privileged IAM Role Audit exists to reverse that drift systematically.
Remote delivery fits this work well: inventory, policy diffs, and verification can be done over secure sessions without on-site access. Fixwebnode covers service areas across the country—see all service areas—and pairs cloud IAM cleanup with Linux host hardening when roles are assumed from servers. For distribution-level server support in Victoria, the Melbourne Linux Experts service is the related path when instance profiles and OS permissions must move together.
Common issues that keep root-level cloud access alive
These problems are distinct. Treat each root cause separately so you do not “fix” one path while leaving another wide open.
1. Automation roles still attached to AdministratorAccess
Symptoms: A Lambda, ECS task, or CI runner can call iam:*, organizations:*, or full *:*. Deploy scripts work “everywhere,” including accounts and regions you never intended.
2. Long-lived access keys with unused or unknown last activity
Symptoms: IAM users (not roles) hold static keys; credential reports show password or key age over 90 days; no one owns the app that still uses them.
3. Wildcard resources and missing condition keys
Symptoms: Policies allow s3:* on *, or sts:AssumeRole without ExternalId, MFA, or source-IP/VPC conditions. Cross-account trust is broader than the partner needs.
4. Privilege escalation via iam:PassRole and attach-policy rights
Symptoms: A “deploy” role cannot be root directly, but it can pass a powerful role to a new EC2/Lambda or attach AdministratorAccess to itself. CloudTrail shows PassRole, CreateRole, or AttachUserPolicy from non-break-glass principals.
How to fix each issue (DIY runbook)
Fix 1 — Strip AdministratorAccess and rebuild least-privilege policies
Inventory roles, detach admin managed policies, and replace them with task-scoped actions. Prefer roles over users. Work in a non-prod account first.
Step 1 — List roles and spot admin attachments
aws iam list-roles --query 'Roles[].RoleName' --output table
aws iam list-attached-role-policies --role-name YOUR_AUTOMATION_ROLE
aws iam list-role-policies --role-name YOUR_AUTOMATION_ROLE
Note any AdministratorAccess, PowerUserAccess, or customer policies with "Action": "*".
Step 2 — Generate a credential and access review baseline
aws iam generate-credential-report
aws iam get-credential-report --query 'Content' --output text | base64 -d > iam-credential-report.csv
aws iam get-account-authorization-details --output json > iam-authz-details.json
Keep these files offline and access-controlled; they map users, roles, and policy links.
Step 3 — Read what the role actually did (90-day window where available)
aws accessanalyzer start-policy-generation \
 --policy-generation-details '{"principalArn":"arn:aws:iam::ACCOUNT_ID:role/YOUR_AUTOMATION_ROLE"}' \
 --cloud-trail-details '{"accessRole":"arn:aws:iam::ACCOUNT_ID:role/AnalyzerAccessRole","trailArn":"arn:aws:cloudtrail:REGION:ACCOUNT_ID:trail/TRAIL"}'
If Access Analyzer policy generation is not set up yet, pull CloudTrail insights for the role session names and list unique API calls instead of guessing permissions.
Step 4 — Detach admin and attach a tight replacement
aws iam detach-role-policy \
 --role-name YOUR_AUTOMATION_ROLE \
 --policy-arn arn:aws:iam::aws:policy/AdministratorAccess

aws iam put-role-policy \
 --role-name YOUR_AUTOMATION_ROLE \
 --policy-name automation-least-privilege \
 --policy-document file://automation-least-privilege.json
Example policy body (edit service, resource ARNs, and conditions to match the real app—never copy wildcards into production blindly):
{
 "Version": "2012-10-17",
 "Statement": [
 {
 "Sid": "QueueAndLogsOnly",
 "Effect": "Allow",
 "Action": [
 "sqs:ReceiveMessage",
 "sqs:DeleteMessage",
 "sqs:GetQueueAttributes",
 "logs:CreateLogStream",
 "logs:PutLogEvents"
 ],
 "Resource": [
 "arn:aws:sqs:ap-southeast-2:ACCOUNT_ID:app-jobs",
 "arn:aws:logs:ap-southeast-2:ACCOUNT_ID:log-group:/aws/lambda/app-worker:*"
 ]
 }
 ]
}
Step 5 — Verify deny of admin paths and allow of required calls
aws iam simulate-principal-policy \
 --policy-source-arn arn:aws:iam::ACCOUNT_ID:role/YOUR_AUTOMATION_ROLE \
 --action-names iam:CreateUser s3:DeleteBucket sqs:ReceiveMessage \
 --resource-arns arn:aws:sqs:ap-southeast-2:ACCOUNT_ID:app-jobs
Expect explicit deny or implicit deny on identity-admin and destructive account actions; allow only the job actions you listed. Re-run the application smoke tests in staging before production cutover.
When to call Fixwebnode: if production cannot tolerate trial-and-error policy edits, or multiple accounts share the same role pattern and you need a coordinated remote audit.
Fix 2 — Eliminate sneaky static keys and force role assumption
Static keys on IAM users are a common “temporary” path that becomes permanent root-adjacent access.
Step 1 — Find old or unused keys
aws iam generate-credential-report
aws iam get-credential-report --query 'Content' --output text | base64 -d \
 | cut -d, -f1,4,9,11,14,16
Focus on users with active keys, password enabled unnecessarily, or last-used dates empty or ancient.
Step 2 — Deactivate before delete
aws iam list-access-keys --user-name LEGACY_BOT
aws iam update-access-key --user-name LEGACY_BOT --access-key-id AKIA... --status Inactive
Watch application errors and CloudTrail for 24–72 hours. If nothing breaks, delete the key and prefer an instance profile, IRSA/workload identity, or OIDC federation for CI.
aws iam delete-access-key --user-name LEGACY_BOT --access-key-id AKIA...Step 3 — Block residual user console/API where roles should own the work
aws iam delete-login-profile --user-name LEGACY_BOT
aws iam attach-user-policy --user-name LEGACY_BOT \
 --policy-arn arn:aws:iam::aws:policy/AWSDenyAll
Only after ownership is confirmed; break-glass users are a separate, monitored exception path—not automation.
When to call Fixwebnode: keys are referenced from unknown repos, vendor appliances, or third-party SaaS you cannot reconfigure alone.
Fix 3 — Kill wildcards and add binding conditions
Broad resources and missing conditions are how a single leaked session becomes multi-bucket, multi-account damage.
Step 1 — Search local policy exports for wildcards
grep -n '"Action": "\*"\|"Resource": "\*"' iam-authz-details.json | head -n 50Step 2 — Rewrite with explicit ARNs and conditions (region ap-southeast-2 is typical for Australian primary workloads). Example trust policy tightening for a partner role:
{
 "Version": "2012-10-17",
 "Statement": [{
 "Effect": "Allow",
 "Principal": {"AWS": "arn:aws:iam::PARTNER_ACCOUNT:root"},
 "Action": "sts:AssumeRole",
 "Condition": {
 "StringEquals": {"sts:ExternalId": "REPLACE_WITH_LONG_RANDOM"},
 "IpAddress": {"aws:SourceIp": "PARTNER_EGRESS_CIDR"}
 }
 }]
}
aws iam update-assume-role-policy \
--role-name PartnerSyncRole \
--policy-document file://partner-trust-tight.jsonStep 3 — Confirm with a failed assume from the wrong context (expect AccessDenied), then a successful assume from the approved path only.
When to call Fixwebnode: multi-account Organizations setups, SCPs conflicting with role policies, or partner contracts that need a clean trust redesign.
Fix 4 — Close privilege-escalation paths (PassRole / attach policy)
A role without AdministratorAccess can still become admin if it can modify identity.
Step 1 — Hunt dangerous actions on deploy roles
grep -E 'iam:(PassRole|AttachRolePolicy|AttachUserPolicy|CreateAccessKey|PutUserPolicy|UpdateAssumeRolePolicy)' \
 -n iam-authz-details.json
Step 2 — Remove identity-admin actions; scope PassRole to specific role ARNs
{
 "Version": "2012-10-17",
 "Statement": [
 {
 "Sid": "PassOnlyWorkerRole",
 "Effect": "Allow",
 "Action": "iam:PassRole",
 "Resource": "arn:aws:iam::ACCOUNT_ID:role/app-worker-role",
 "Condition": {"StringEquals": {"iam:PassedToService": "ecs-tasks.amazonaws.com"}}
 },
 {
 "Sid": "DenyIdentityAdmin",
 "Effect": "Deny",
 "Action": [
 "iam:CreateUser",
 "iam:CreateAccessKey",
 "iam:AttachRolePolicy",
 "iam:AttachUserPolicy",
 "iam:PutRolePolicy",
 "iam:UpdateAssumeRolePolicy",
 "iam:CreatePolicyVersion"
 ],
 "Resource": "*"
 }
 ]
}
Step 3 — Re-simulate and review CloudTrail
aws iam simulate-principal-policy \
 --policy-source-arn arn:aws:iam::ACCOUNT_ID:role/deploy-role \
 --action-names iam:PassRole iam:AttachUserPolicy \
 --resource-arns arn:aws:iam::ACCOUNT_ID:role/app-worker-role

aws cloudtrail lookup-events \
 --lookup-attributes AttributeKey=EventName,AttributeValue=PassRole \
 --max-results 20
Investigate any PassRole or policy-attach events outside change windows.
When to call Fixwebnode: you already see unexpected PassRole/CreateUser events, logging gaps, or you need emergency containment plus lasting least-privilege redesign.
When DIY is enough vs when to book Fixwebnode
DIY is enough when you have staging clones, CloudTrail is complete, you can name every workload owner, and a rollback plan exists for each policy change. Work one role at a time, simulate, smoke-test, then promote.
Book Fixwebnode when admin policies are tangled across many accounts, production outages are unacceptable during policy shrink, keys are embedded in unknown systems, or you need a remote specialist to pair IAM stripping with server and control-plane hygiene. Fixwebnode is a direct provider—not a freelance marketplace—so you speak with the people doing the work. Individuals, sole traders, and local operators can open the conversation via https://fixwebnode.com.au/website-repair-australia.
Enforce least privilege as an ongoing control
After the initial Over-Privileged IAM Role Audit, schedule recurring checks: credential reports monthly, Access Analyzer findings weekly, and mandatory expiry for any break-glass elevation. Prefer short-lived federation over static keys. Deny identity-admin actions on all non-security roles by default. Keep Australian primary resources region-scoped (for example ap-southeast-2) unless multi-region is a documented requirement.
Talk to Fixwebnode about your IAM audit
If a minor automation principal still holds sneaky root-equivalent rights, do not wait for a compromise to force the cleanup. Fixwebnode can remotely inventory roles, strip over-broad policies, and help you lock least privilege into day-to-day operations across your cloud footprint in Australia. Review coverage on the service areas page, then book a conversation through the landing page for individuals and local operators: Fixwebnode website repair Australia. Bring your account IDs, role names, and any recent CloudTrail anomalies—we will start from the blast radius, not from a generic checklist.