
 Multi-Vendor & Complex SaaS Marketplaces
 Modern Headless & Jamstack Web Development
 High-End Corporate & Specialized Business Websites
 Advanced API, Checkout & Database Troubleshooting
Hide Origin IP Behind Reverse Proxy: Server Anonymity Guide
Mask your origin server IP with edge reverse proxies, firewall isolation, and integrity checks. Practical DIY steps for Australian hosts—plus when Fixwebnode should take over remotely.
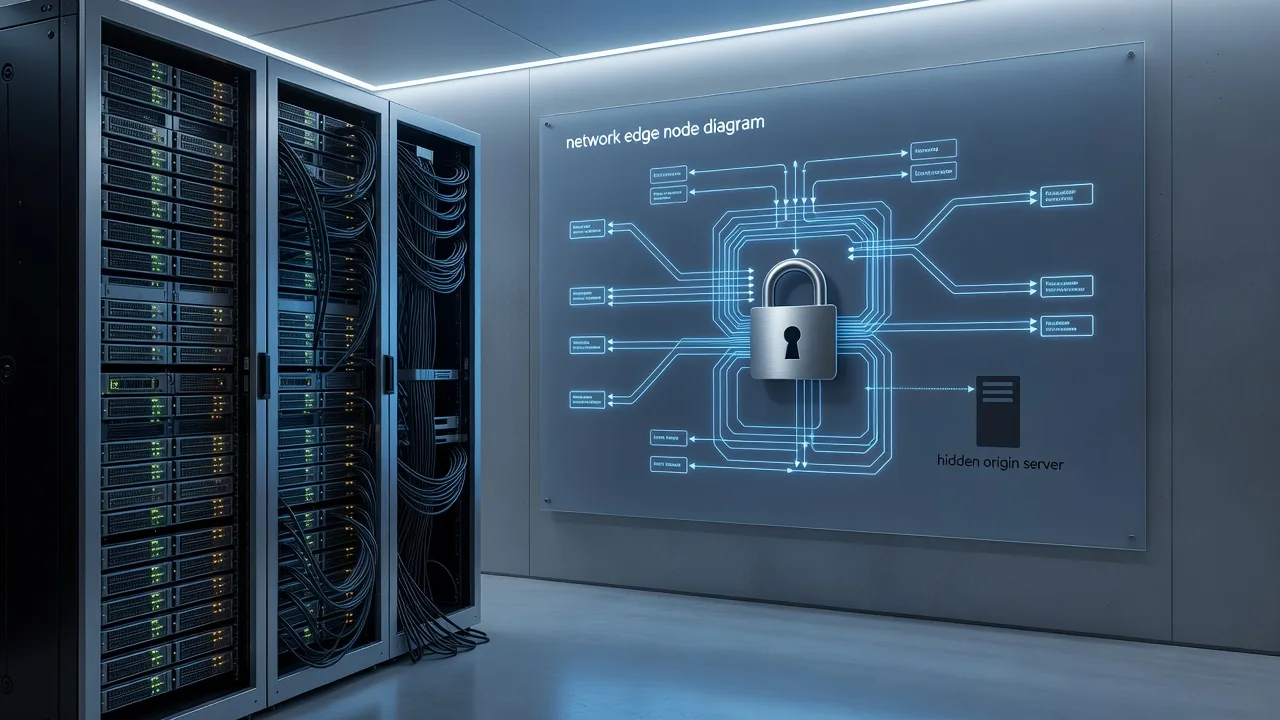
If scanners, bots, or competitors can resolve your real host IP, a reverse proxy alone will not protect you—direct attacks still hit the origin. This guide walks Australian site owners and small-business sysadmins through total server anonymity: edge interception architecture, masking and isolating the host IP, and locking down network integrity profiles with real commands and configs. For hands-on remote help on Ubuntu/Linux stacks, start with Fixwebnode Linux server support.
Scope assumes a typical VPS or dedicated host (Ubuntu 22.04/24.04), Nginx or Caddy as origin web server, and a public edge (Cloudflare, another reverse proxy VPS, or self-hosted Nginx edge). Work is fully remote/digital—no on-site visit required.
Why origin IP anonymity matters for Australian servers
DNS, mail headers, old A records, SSL transparency logs, and misconfigured firewalls routinely leak the backend address. Once leaked, volumetric floods and exploit scanners bypass your edge. Edge interception means all public traffic terminates at a proxy layer that forwards only trusted requests to a private origin. Your job is threefold: put a clean edge in front, stop the world from reaching the origin on 80/443, and continuously verify that the real IP stays off public resolution paths.
Fixwebnode provides direct remote server support across Australia for this exact stack—proxy design, firewall isolation, and integrity hardening—not a freelance marketplace. See where remote coverage applies on our service areas page.
How do I hide my origin server IP behind a reverse proxy in Australia?
Point public DNS only at the edge proxy, allow origin web ports solely from the proxy’s egress IPs, and purge historical A/AAAA records and side channels (mail, subdomains, staging). Verify with external lookups and direct-connect tests that port 443 on the origin refuses the public internet. If DNS still answers with the VPS address or the origin accepts random clients, isolation is incomplete and needs a controlled firewall and DNS audit.
| Symptom | Quick fix | When to call Fixwebnode |
|---|---|---|
| Origin IP still in DNS | Remove A/AAAA; orange-cloud or edge-only records | Legacy zones, DNSSEC, or multi-registrar mess |
| Direct HTTPS to origin works | UFW/iptables allowlist proxy IPs only | Cloud firewall + panel conflicts, locked out SSH |
| IP leak via mail/API subdomain | Separate hosts; no shared origin A record | Complex mail + app mesh on one box |
Architecture of edge interception (what “total” anonymity actually means)
Public clients resolve only the edge. The edge terminates TLS (or passes through carefully), adds forwarding headers, and connects to the origin over a restricted path. The origin never publishes its address in public DNS for web hostnames. Host firewall and provider security groups drop world traffic on 80/443. Integrity profiles mean you can prove—on a schedule—that DNS, firewall, and proxy trust rules still match the design.
Minimal reference layout
- Edge: Cloudflare proxy, or a small Nginx/Caddy VPS in a region you choose
- Origin: application VPS with private allowlist
- Admin path: SSH on a non-default port or VPN/WireGuard only
- DNS: apex and www only at edge IPs or proxied records
Common issues when masking the origin IP
1. DNS and history still expose the real A record
Symptom: dig +short yourdomain.com from a home connection returns the VPS address, or security scanners report the same IP as months ago despite “proxy on.”
2. Origin still accepts direct client connections on 80/443
Symptom: browsing https://ORIGIN_IP shows your site or certificate; floods against the IP ignore Cloudflare/edge entirely.
3. Proxy headers and real-IP trust are wrong (or forged)
Symptom: app logs show edge IP for every user, rate limits break, or clients spoof X-Forwarded-For because the origin trusts the world.
4. Side channels re-leak the host (mail, staging, API, IPv6)
Symptom: SPF/MX research, staging. subdomain, or an AAAA record still points at the same machine you locked down on IPv4.
Step-by-step: mask and isolate the host IP
Issue A — Purge public DNS and pin traffic to the edge
Goal: no public web hostname resolves to the origin.
- Inventory current answers from a network outside your VPS:
dig +short A yourdomain.com @1.1.1.1
dig +short AAAA yourdomain.com @1.1.1.1
dig +short A www.yourdomain.com @1.1.1.1
whois $(dig +short A yourdomain.com @1.1.1.1 | tail -1)
Confirm whether the address is your origin or the edge.
- At your DNS host, set apex/www to the edge only (Cloudflare proxied/orange-cloud, or A/AAAA of your reverse-proxy VPS). Delete leftover A/AAAA pointing at the origin for web names.
- Check passive leak sources: old DNS providers, subdomain takeover leftovers, monitoring tools that registered the raw IP, and certificate SANs on forgotten hosts.
- Re-test after TTL:
dig +short A yourdomain.com @8.8.8.8
dig +short A yourdomain.com @1.1.1.1
Both should show edge addresses only. If the origin IP remains, you still have a published record or a second zone authority.
When to book Fixwebnode: conflicting DNSSEC, split zones across registrars, or automated panels rewriting records after you fix them.
Issue B — Firewall the origin so only the edge can speak HTTP(S)
Goal: world clients cannot open 80/443 on the origin even if they know the IP.
Step 1 — List listening services
sudo ss -tulpn | egrep ':80|:443|:22'
sudo ufw status verbose
Step 2 — Allowlist model (UFW example). Replace EDGE_IP with your proxy egress address (or Cloudflare published IP ranges managed carefully). Keep SSH available from your admin IP before enabling the default deny.
sudo ufw default deny incoming
sudo ufw default allow outgoing
sudo ufw allow from ADMIN_IP to any port 22 proto tcp
sudo ufw allow from EDGE_IP to any port 80 proto tcp
sudo ufw allow from EDGE_IP to any port 443 proto tcp
sudo ufw enable
sudo ufw status numbered
For Cloudflare-only origins, prefer provider firewall + documented Cloudflare IP ranges, and reload ranges when they change—do not guess.
Step 3 — Verify isolation from a third network (phone LTE or an external VPS):
curl -vk --connect-timeout 5 https://ORIGIN_IP/
nc -vz ORIGIN_IP 443
Expected: timeout or refuse from the public internet; success only via the domain through the edge.
Step 4 — Origin Nginx: trust real client IP only from the edge
# /etc/nginx/conf.d/realip.conf
set_real_ip_from EDGE_IP;
# or Cloudflare ranges via include
real_ip_header CF-Connecting-IP;
# use X-Forwarded-For only if the edge is under your control
# real_ip_header X-Forwarded-For;
real_ip_recursive on;
sudo nginx -t && sudo systemctl reload nginxWhen to book Fixwebnode: you risk locking yourself out, run Docker-published ports that bypass UFW, or need cloud security groups aligned with host iptables.
Issue C — Build a correct reverse-proxy edge (interception layer)
Goal: TLS and HTTP terminate at the edge; origin receives only proxy traffic.
Example: Nginx edge → origin
# /etc/nginx/sites-available/edge-origin
server {
 listen 443 ssl http2;
 server_name yourdomain.com www.yourdomain.com;

 ssl_certificate /etc/letsencrypt/live/yourdomain.com/fullchain.pem;
 ssl_certificate_key /etc/letsencrypt/live/yourdomain.com/privkey.pem;

 location / {
 proxy_pass https://ORIGIN_IP:443;
 proxy_http_version 1.1;
 proxy_set_header Host $host;
 proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
 proxy_set_header X-Forwarded-Proto $scheme;
 proxy_set_header Connection "";
 proxy_ssl_server_name on;
 proxy_ssl_name yourdomain.com;
 }
}
sudo ln -s /etc/nginx/sites-available/edge-origin /etc/nginx/sites-enabled/
sudo nginx -t && sudo systemctl reload nginxOrigin should reject non-proxy Host abuse (optional allowlist snip):
# on origin server block
allow EDGE_IP;
deny all;
Place that inside the server listening on 443 if you want belt-and-braces beyond UFW.
Verify through the edge
curl -I https://yourdomain.com
curl -s https://ifconfig.me # run on origin; note IP — must not appear in public dig
Issue D — Securing network integrity profiles
Integrity means continuous proof that anonymity controls did not drift.
- Baseline the public view (store in your runbook):
dig +short A yourdomain.com @1.1.1.1 | tee /root/integrity/dns-web.txt
curl -sI https://yourdomain.com | tee /root/integrity/headers.txt- Confirm origin ports from outside on a schedule (cron on a separate monitor host):
#!/bin/bash
# monitor host — expect FAILURE on direct origin HTTPS
if nc -zw3 ORIGIN_IP 443; then
 echo "ALERT: origin 443 reachable" | mail -s "IP anonymity breach" you@example.com
fi- Lock down IPv6 the same way as IPv4 (common Australian VPS leak):
ip -6 addr
sudo ufw deny in on eth0 proto tcp to any port 80
# prefer explicit v6 allowlists mirroring v4, or disable public AAAA for origin- Separate mail and web: MX and SPF should not force the web origin IP onto investigation paths if you can use a mail provider or dedicated mail host.
- Strip outbound identity leaks where apps call external APIs: egress via NAT/proxy if the origin IP must stay obscure to third parties (understand limits—true hiding from determined parties needs careful threat modelling).
- Reload edge certificates and services cleanly:
sudo certbot renew --dry-run
sudo systemctl status nginx
sudo journalctl -u nginx -n 50 --no-pager
When to book Fixwebnode: you need a monitored integrity profile, multi-edge failover, or coordinated changes with hosting panels without downtime.
DIY checklist vs booking Fixwebnode
DIY is enough when you control DNS, can maintain UFW/security groups, have console/IPMI access if SSH breaks, and a single origin behind one edge. Follow the numbered steps above, keep an admin allowlist, and re-test after every DNS or firewall change.
Book Fixwebnode when direct origin access still works after your rules, Docker/Kubernetes publishes bypass ports, IPv6 or mail re-leaks the host, you face active floods on a leaked IP, or you need a full edge design reviewed remotely. We work as a direct specialist team for Australian businesses—not a bid board. Software rollout on related workstations can be coordinated via our Melbourne software installation experts service when desktop and server changes must land together.
Closing: keep the origin off the public map
Total server anonymity is not a single Cloudflare tickbox. It is edge interception, DNS discipline, strict origin allowlists, correct real-IP trust, and integrity checks that catch drift—especially IPv6 and forgotten subdomains. Use the commands above to mask and isolate the host IP, then verify from a network that is not your server.
If you want a remote architecture review, firewall isolation done without lockout, or an integrity profile maintained for your stack in Australia, start a conversation with Fixwebnode via the Linux server support landing page. Tell us your edge provider, OS version, and whether the origin IP is already circulating—we will map the safest sequence before any cutover.